ENGLISH EDITION · 議題探討
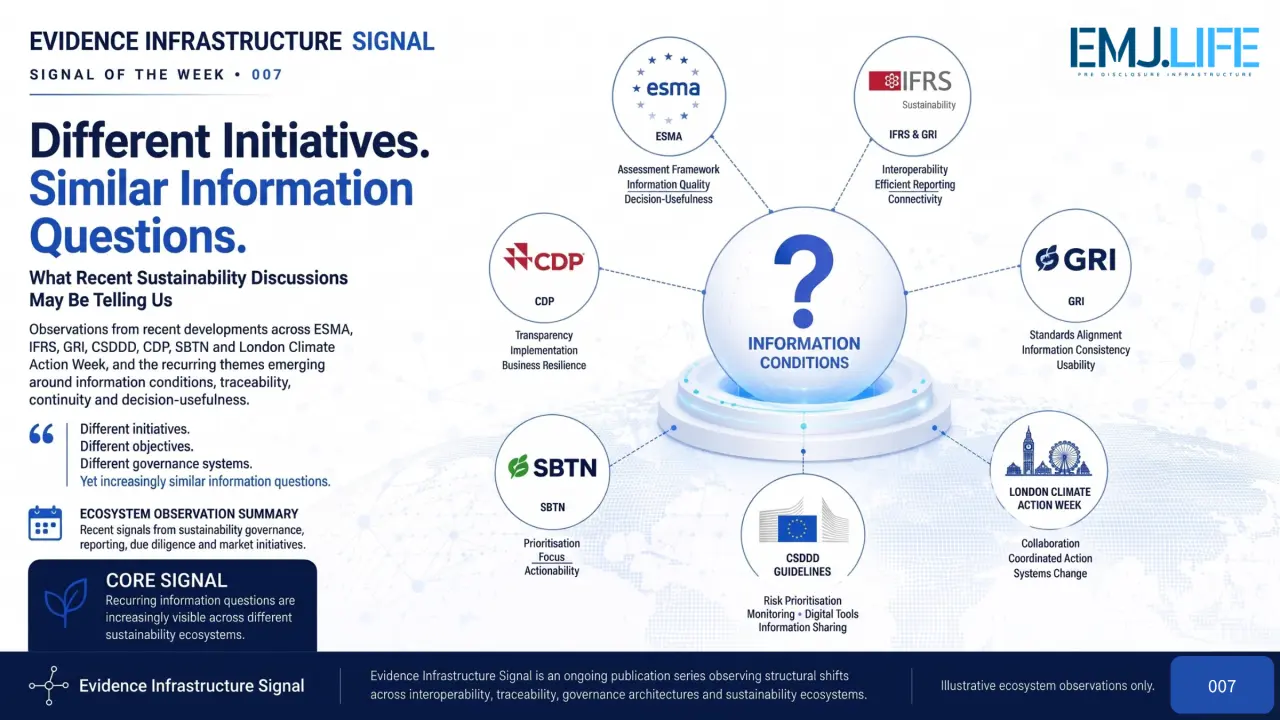
Different Initiatives. Similar Information Questions.
Why Information Conditions Are Becoming Increasingly Visible Across Sustainability Ecosystems
This English edition is available for independent reading and search discovery.
Executive Summary / Lead
Recent initiatives in reporting, due diligence, governance and digital systems appear separate but increasingly focus on whether information can remain usable over time. The common signal is that enforcement, interoperability, due diligence, corporate governance and target setting no longer ask only what should be disclosed. They increasingly ask how information is identified, formed, maintained, shared and trusted. Institutional friction therefore moves from differences in standards to whether data retain provenance and purpose across decision environments. This Signal treats the movement of different initiatives from disclosure content to information formation and governance as a direction emerging across institutional actions, not as a joint programme announced by any one authority. Legal status, publication date and population remain source-specific. Cross-reading supports a directional judgement only; similar language must not be converted into a single obligation. To make the lead decision-ready, it answers five questions together: what has occurred, which first-party record supports it, through what mechanism the effect may travel, which outcome evidence is still missing, and what next observation could strengthen or overturn the judgement. Any causal relationship not stated by the source remains an editorial inference and is not converted into a factual claim through confident wording.
Company & Industry Context
ESMA, the IFRS Foundation and GRI, EU due diligence, CDP and SBTN approach information through regulation, interoperability, risk, governance and target setting. ESMA addresses enforcement of corporate reporting, IFRS and GRI address complementarity, EU due diligence connects value-chain risk, and CDP and SBTN address governance and prioritisation. They use different evidence but each needs to know who produced data, which activity it covers, how it changes and whether it supports the specified judgement. Convergence is not established by repeated vocabulary. It is established when independent institutions begin to require comparable capabilities around identity, origin, method, accountability, control and version. Every source retains its own authority and time reference so that comparison does not become a claim of institutional merger. Time and authority must also be separated. An announcement date is not an effective date; a pilot is not general adoption; a technical specification is not a legal obligation; and voluntary enterprise use is not regulatory approval. Putting these events on one timeline shows when an institutional development actually enters data, contract, investment or disclosure processes and which actor is authorised to make that transition.
Challenge / Why It Matters
The question is no longer only what to disclose, but how risks are identified, priorities set, and information kept traceable, comparable and decision-useful. Inside organisations, information is often divided: legal teams hold obligations, sustainability teams manage metrics, procurement obtains supplier declarations and IT controls access. As data cross departments, authority, version and consent can disappear. The downstream user sees consistent format but cannot reconstruct how risk identification or prioritisation was formed. When upstream evidence lacks stable identity, formation time, applicable boundary and version, a standardised output may still be impossible to reconstruct. The material risk is not one missing field. It is the silent conversion of the wrong entity, an expired method, an inferred relationship or an unapproved version into an apparent fact as information moves downstream. Concrete failure modes include incorrect entity matching, an incomplete data population, inconsistent boundaries, unversioned methods or factors, exceptions without rationale, approval occurring after publication, and downstream reuse outside the original purpose. Each failure can turn a reasonable individual record into a conclusion that cannot be defended after aggregation, comparison or machine-assisted interpretation.
Action / Solution / Implementation
Governance needs to cover information formation, maintenance, sharing and trust through traceability, interoperability, continuity, comparability, usability and control. An information formation record connects requirement, source, method, owner, approval, sharing permission, decision use and update state. When data are proposed for a new framework, customer or regulatory purpose, a purpose and boundary check determines whether reuse is valid, supplementation is required or new formation is necessary. The implementable control unit is a governed evidence object. Each material claim links to its primary source, calculation or judgement method, organisational and temporal boundary, accountable owner, control state, exception, approval and version. When any component changes, the system preserves the difference and affected uses instead of overwriting the earlier basis. A minimum operating control set includes a claim register, evidence owner, source snapshot, method identity, valid period, control frequency, exception threshold, review, approval and permitted downstream use. High-judgement or high-financial-impact items receive a stronger review tier. Lower-risk records use automated completeness and consistency checks so that governance effort is concentrated where a wrong claim would change a decision.
Evidence / Results / Impact
The edition reviews ESRS technical advice, IFRS-GRI interoperability, the CSDDD implementation consultation, CDP governance observations and SBTN prioritization. The publications support the observation that multiple initiatives are focusing on implementation and information governance. They do not establish one common process. SNN's shared information problem is an analysis of cross-regime friction and does not treat enforcement, due diligence, target setting and corporate governance as interchangeable institutions. Evidence is assessed through source comparison rather than a simple source count. Documents that repeat one underlying dataset remain one evidential path. Similar requirements from independent institutions can strengthen a directional signal, but they do not prove implementation results, legal equivalence or equal market maturity. Every material sentence should enter a claim ledger and be classified as official fact, direct measurement, estimate, corporate commitment, delivered outcome or SNN editorial inference. The ledger records the precise scope that each source supports. Conflicting evidence is retained with the resolution rationale; absent evidence is marked pending rather than filled with a convenient analogue from another entity, period or jurisdiction.
Industry & Institutional Implications
The cross-system priority is moving from reducing differences among standards toward reducing information friction between them. When formation is visible, a decision-maker receives not only a number but also priority, exception and uncertainty. Data investment becomes reusable operating capability rather than a reporting project, and a changed regulator or customer requirement can identify affected evidence without recollecting the entire dataset. The purpose of this information density is not length for its own sake. It is to shorten the verification distance between claim and decision. Boards, investors, regulators and operational teams should be able to distinguish fact, estimate, commitment, progress and outcome, then update the judgement when conditions change without reconstructing the case from scattered files and oral explanation. Accountability therefore attaches to decision rights. The data owner maintains the source, the method owner controls calculation, the business function defines the use case, internal control or assurance tests reproducibility, and the approver accepts responsibility for final use. An exception without an expiry date, remediation owner and impact scope stops being temporary treatment and becomes persistent evidence debt.
SNN Editorial / Pre-Disclosure Evidence Infrastructure Perspective
SNN editorial analysis: EU due-diligence, digital-product-data and corporate-governance initiatives create a shared pressure on Taiwan electronics, textile, machinery and consumer-goods supply chains. Companies need provenance, maintenance responsibility and permissions embedded in procurement, production, quality and customer-delivery workflows rather than assembled only at disclosure. Taiwan electronics, textile, machinery and consumer-goods supply chains facing EU due diligence, digital-product and customer-governance requests should connect supplier identity, consent, risk judgement, audit, remediation and data sharing. Evidence absent from procurement and production cannot be recreated by a complete English report at the disclosure endpoint. For Taiwan, relevance should be traced through an actual transmission path. An international rule or customer requirement first enters finance, procurement, contract, supplier-data and assurance processes, then changes local systems and controls. It does not automatically become Taiwan law. Companies need to identify the applicable scenario, preserve bilingual mappings and make the evidence chain reviewable under controlled access. Taiwan companies can perform the transmission test on concrete objects: the company and legal entity, facility, product, batch, supplier, contract, financing instrument and disclosure field. Chinese and English names, internal and external classifications and different reporting frameworks should resolve to the same claim identity. Traceability must still preserve commercial confidentiality, personal data and access boundaries; it does not require unrestricted publication.
Future Outlook
Future implementation should be evaluated through due-diligence tools, third-party verification and repeatable information sharing across standards. Future evidence should test whether digital due-diligence tools, third-party verification and data sharing preserve purpose and permission. A low-regret action is to sample one item used by three departments, reconstruct its production, transformation, approval and sharing, and repair any node unable to explain purpose or version. Future monitoring should separate final text, technical guidance, adoption scope, operating controls, supervision and observable outcomes. A low-regret step is to select one high-risk claim for an end-to-end reconstruction test and record missing identity, source, method, accountability and version. That is governance preparation, not a compliance guarantee or forecast of results. Monitoring should be event-triggered as well as calendar-based. A final rule, amended technical guidance, expanded scope, supervisory action, adoption data or observed outcome creates a new version and a reassessment of the earlier judgement. The prior conclusion is not erased. It retains its original basis, identifies the new evidence that changed it and states which decisions or downstream uses now require review.
Sources, evidence chain and editorial responsibility
Source publication: sustainabilitynewsnetwork.net · Original author: Anderson Yu · Original publication date:
Original publication
External institutional and reporting sources
These external announcements, rules, studies and reports support the discussion and are displayed separately from the original publication.
- Primary analysis sourceESMAEnforcement of Corporate Reporting ↗Published date not provided · Accessed 2026-08-16 19:26:49
Official primary source selected through publication-level web research.
- Taiwan market-context source臺灣證券交易所ESG生態系專區上線 引領永續新價值 ↗Published 2026-03-23 · Accessed 2026-08-25
Supports Taiwan implementation across digital filing, formatted sustainability information, assurance, ESG evaluation and AI-assisted review.
Topic hub: Pre-Disclosure Evidence Infrastructure