議題探討
EIA-025|代理者不是權限:台灣企業 AI 自主執行的委任、採購與問責證據
SNN.TW 制度解讀SNN.TW Institutional Interpretation
AI 代理者能執行採購或系統動作,並不因此取得企業授權。本文從 NIST、FSB 與 ICO 的不同制度狀態出發,核對台灣人工智慧基本法、金融指引、公司權限與個資邊界,提出上市櫃、製造與金融業在揭露前應保留的委任、執行時授權及獨立審查證據。
本文身分與雙語引用
Article identity and bilingual citation
- 內容身分 Identity
- SNN.TW 台灣獨立解讀 · SNN.TW 制度解讀Independent Taiwan interpretation · SNN.TW Institutional Interpretation
- 語言 Languages
- 繁體中文及英文同頁 · 同一本站 canonicalTraditional Chinese and English on the same local canonical
- 發布/版本 Published / version
- 2026-11-09T16:00:00.000Z · v8 · 更新 2026-11-10T15:42:41.993Z2026-11-09T16:00:00.000Z · v8 · Updated 2026-11-10T15:42:41.993Z
- 本站正典 Local canonical
- https://snn.tw/article/eia-025-the-agent-is-not-the-authority
- 全球脈絡 Global starting point
- EIA-025 · sustainabilitynewsnetwork.net ↗Starting point for independent Taiwan interpretation; no translation equivalence asserted.
Publisher/編輯責任:SNN.TW。樞紐閱讀:台灣永續揭露、AI 治理與採購、供應鏈與人權盡職調查、永續金融與投信治理。Publisher and editorial controller: SNN.TW.
台灣法律與政策狀態
Taiwan legal and policy state, by source
本文編輯判讀:《人工智慧基本法》已公布施行;行政院施行規劃是政策公告,數發部風險框架是行政評估工具。金管會 AI 與身分指引各有金融業適用邊界;公司法、電子簽章法的正式法規須依個案適用。個資法 2025 年修正部分條文尚未生效。
The AI Basic Act is in force. The Executive Yuan plan is an announcement and the digital ministry framework an administrative assessment tool. FSC guidance has financial-sector limits; operative Company Act and Electronic Signatures Act provisions require transaction-specific application. Parts of the 2025 privacy amendment remain uncommenced.
現行具拘束力規則 CURRENT_BINDING_RULECurrent binding rule
文件日期:2026-01-14 · 查核日期:2026-11-10T15:33:21.821Z
支持範圍:基本法原則及公部門適用條文
限制:正式法規;不得推成所有民間 AI 代理動作均有同一直接法定核准程序
已公告變動 ANNOUNCED_CHANGEAnnounced change
文件日期:2026-05-21 · 查核日期:2026-11-10T15:33:21.821Z
支持範圍:政策施行及調適時程公告
限制:新聞公告並非各產業已完成修法或直接企業義務
僅供背景參考 CONTEXT_ONLYContext only
文件日期:2026-07-07 · 查核日期:2026-11-10T15:33:21.821Z
支持範圍:行政框架作為主管機關共通評估語言
限制:框架生效不表示所有企業取得同一直接法定義務;仍看目的事業法規
顯示 3/10 筆台灣官方來源。Showing 3 of 10 Taiwan institutional sources.
本卡不宣稱整篇文章的單一法律狀態,也不是法律意見或合規判定。來源日期不是生效日。No aggregate legal conclusion, legal advice or compliance determination. A document date is not an effective date. 第 07 段/Section 07 → 完整來源鏈/Full evidence chain →
台灣傳導判讀
- 事件與本文範圍
- 有效憑證不等於有效企業委任。
- 制度狀態
- 《人工智慧基本法》已公布施行;行政院施行規劃是政策公告,數發部風險框架是行政評估工具。金管會 AI 與身分指引各有金融業適用邊界;公司法、電子簽章法的正式法規須依個案適用。個資法 2025 年修正部分條文尚未生效。
- 台灣路徑與有權角色
- 第 07 段說明本文的市場傳導、對象與可執行職能。前往第 07 段 →
- 不得推論
- 本篇禁止推論:代理者登入成功並完成訂單,不證明任務發起人有公司授權、付款有效或成果已獲審查。
全球原始分析、台灣證據鏈與本站編輯解讀分別標示;下方來源可供核對,並不代表來源機構認可本篇結論。
Taiwan legal and sourcing boundary
Event and scope: A valid credential does not establish a valid corporate mandate.
Taiwan state: The AI Basic Act is in force. The Executive Yuan plan is an announcement and the digital ministry framework an administrative assessment tool. FSC guidance has financial-sector limits; operative Company Act and Electronic Signatures Act provisions require transaction-specific application. Parts of the 2025 privacy amendment remain uncommenced.
Market transmission: Global agent identity and financial governance developments can flow through overseas buyer contracts, bank review and supply-chain access controls to Taiwan manufacturing, technology, financial and listed companies as demands for mandate, order, payment and pre-disclosure evidence. Read Section 07 →
Do not infer: Prohibited inference for this edition: A successful login and completed order do not prove that the task originator held corporate authority, that payment was valid or that an outcome was reviewed.
The Agent Is Not the Authority: Delegation and Accountability for AI Actions in Taiwan
An AI agent can execute a procurement or system action without holding the enterprise authority for it. This independent Taiwan interpretation separates emerging NIST design tenets, FSB sound practices and an ICO consultation from Taiwan law, sector guidance, corporate mandates and personal-data duties, identifying pre-disclosure evidence for listed issuers, manufacturers and financial institutions.
重點摘要
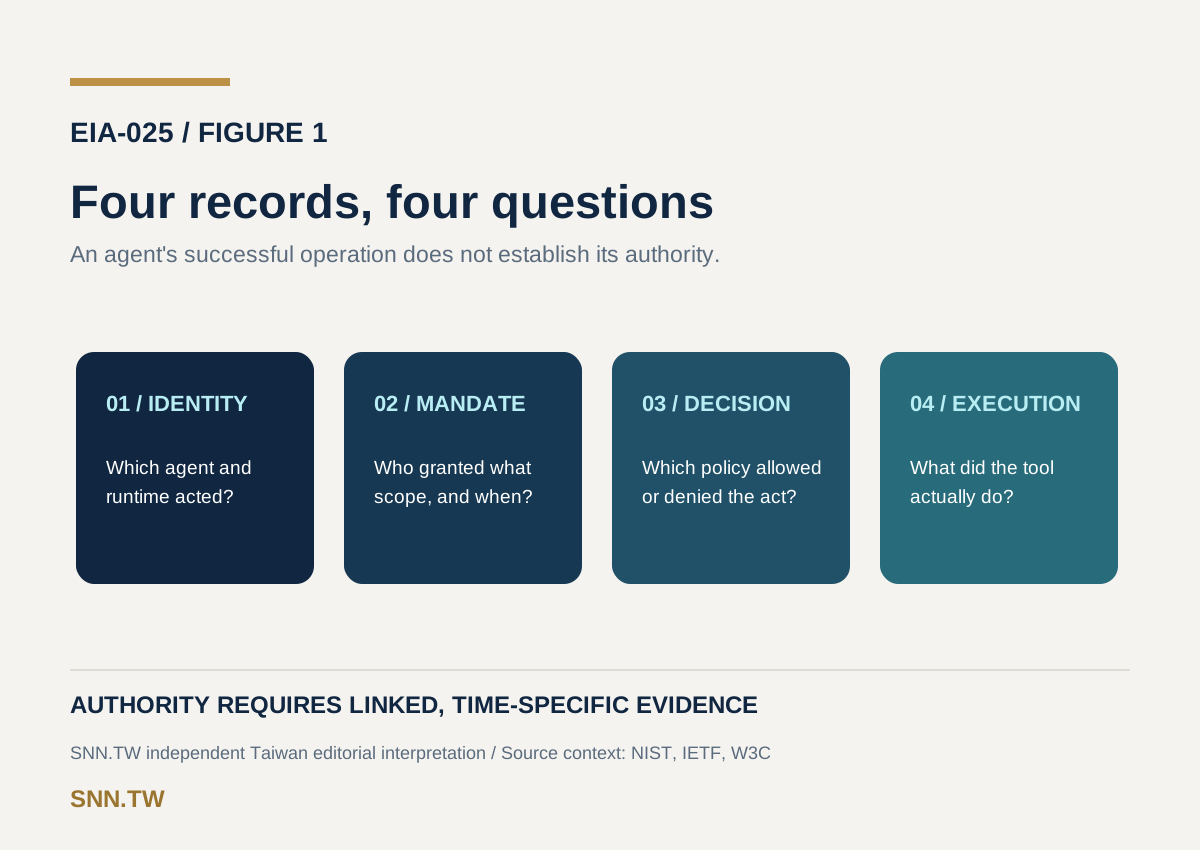
Executive Summary / Lead全球 EIA-025 問的是代理者已完成操作後,誰能證明該操作在當時、對該對象及用途仍有有效授權。NIST 於 2026 年 10 月提出十項代理身分設計原則;FSB 同月公布金融機構 AI 治理的十二項非強制實務;英國 ICO 正徵詢代理式 AI 的個資問題。[1–4] 三者不是同一套全球法定授權標準。SNN.TW 的台灣獨立解讀沿著企業採購、金融服務及上市櫃內控程序,將代理身分、公司委任、執行時政策決定、工具操作及事後審查分成五種證據。台灣《人工智慧基本法》已施行,但並未把所有企業代理操作統一規定為同一種法定核准流程。[10–12]
Global EIA-025 asks who can demonstrate that an AI agent's completed action remained authorised for that actor, purpose and moment. In October 2026, NIST proposed ten initial agent identity design tenets; the FSB issued twelve non-binding sound practices for financial institutions; and the UK ICO opened a consultation on agentic AI and personal data. [1–4] These institutions have not issued one global statutory agent-authorisation regime. This SNN.TW independent interpretation follows Taiwan procurement, financial services and listed-company controls. It separates agent identity, corporate mandate, runtime policy decision, tool execution and competent review as five distinct evidence questions. Taiwan's AI Basic Act is in force, but it does not itself prescribe one identical authorisation procedure for every private-enterprise agent action. [10–12]
企業與產業背景
Company & Industry Context台灣企業可能讓 AI 代理者比較供應商、草擬採購單、呼叫 ERP API、處理金融客戶資料或提交程式部署請求。跨境採購方會詢問誰發出任務、採購額度和供應商範圍如何限制,以及誰能撤銷授權。這些屬具體交易與契約審查,不是 NIST 技術部落格直接在台灣創設的義務。[1] 國科會公布的《人工智慧基本法》提供已生效的基本法框架,行政院施行規劃與數發部風險分類框架分別說明後續部會調適及共同評估語言,仍須區分法條、公告和行政工具。[10–12] 金管會 AI 指引及核心原則針對金融業提供治理參考;數位身分驗證指引主要涉及自然人金融服務,不能替企業代理者的公司權限背書。[13–15] 公司法的董事會、經理人權限與企業章程、決議和委任關係,才是個案權限調查不可略過的層次。[17]
A Taiwan enterprise may let an AI agent compare suppliers, draft purchase orders, call an ERP API, process financial-customer data or propose a software deployment. An overseas buyer may ask who initiated the task, how supplier and spending limits were set, and how authority can be revoked. These are transaction and contract questions; NIST's technical blog does not itself create a Taiwan legal duty. [1] Taiwan's AI Basic Act supplies the enacted statutory framework. The Executive Yuan's implementation plan and the Ministry of Digital Affairs risk-classification framework describe later sectoral adaptation and a common government assessment language. The law, announcement and administrative framework retain separate states. [10–12] FSC AI principles and guidance address the financial sector. Its digital-identity guidance principally concerns natural persons using financial services and cannot certify an AI agent's corporate mandate. [13–15] Taiwan Company Act provisions on boards and managers, together with the actual articles, resolutions and delegation instruments, remain material to a transaction-specific authority inquiry. [17]
挑戰與重要性
Challenge / Why It Matters第一個錯誤是把可登入等同可下單。NIST 零信任架構與 IETF 代換權杖可記錄身分及代行關係,但合法取得 token 不證明任務發起人擁有該項公司權限。[5–6] 第二個錯誤是把成功 API 回應當成已批准的商業決策。代理者可能越過額度、選錯交易對象、沿用已撤回的委任,或把供應商文件內的不可信指令當作新的授權。第三個錯誤是把不可竄改紀錄當成真實或完整。W3C 的來源關係模型與可驗證憑證支援重建和驗簽,卻不判定每筆主張的實質真偽。[7–8] 台灣企業如將操作紀錄含個資長期保存,還需區分當下有效的個資法條與 2025 年修正後尚未施行的條文,核對蒐集目的、存取與保存必要性。[19] 這不是要求每一步都由人手批准,而是防止形式上的批准按鈕遮住真實的權責缺口。
The first failure is treating login capability as order authority. NIST zero-trust architecture and IETF token exchange can support attribution and delegation representation, yet a valid token cannot show that the task originator had the requisite corporate power. [5–6] The second is reading a successful API response as an approved commercial decision. An agent may exceed a threshold, choose an ineligible supplier, use a revoked mandate or interpret instructions embedded in an untrusted supplier document as a new grant of authority. The third is treating a tamper-evident record as necessarily complete and true. W3C provenance and verifiable-credential models can help reconstruct relationships and verify signatures, without determining every underlying claim's substantive validity. [7–8] If a Taiwan enterprise stores extensive logs containing personal data, it must distinguish currently operative Personal Data Protection Act provisions from parts of the 2025 amendment whose commencement remains undetermined, and examine purpose, access and retention. [19] Meaningful oversight is risk-based; it is not established by a button that reviewers approve routinely.
行動、方案與執行
Action / Solution / Implementation受控實作可從一張代理工作範圍表開始:記錄企業法律主體、授權職位、任務目的、代理者與運行版本、可用工具、資料類別、交易額度、對象、有效期、升級門檻及撤銷條件。董事會或有權管理階層核定高風險的委任邊界;法務核對章程、決議、契約及代理關係;採購在供應商名單、額度和付款資料上設定不可由代理者自行改寫的控制。[1,5–6,17] 資安及產品團隊以獨立的政策決定點在每次關鍵工具呼叫時檢查當時權限,保留允許、拒絕及人工升級的版本、時間和理由。財務對付款及會計過帳保有自己的核准鏈,不能因代理者可建立採購單就推定其可放行付款。內部稽核定期抽查任務發起、權杖、政策、操作回應與例外處理是否能串回同一法律主體和有效期間。代理者可自動處理低風險範圍內工作,高風險或超界事件由適格人員重新授權;過密的批准提示也須評估審查疲乏。[1,3] 電子文件或簽章的法律效果仍取決於台灣《電子簽章法》的適用條件,不能由系統日誌自行推定。[18]
A controlled implementation begins with a mandate register: legal entity, authorising office, task purpose, agent and runtime version, permitted tools and data, supplier class, spending ceiling, validity period, escalation threshold and revocation route. The board or authorised management defines high-risk delegation boundaries. Legal reviews articles, resolutions, contracts and delegation instruments. Procurement configures supplier, amount and payment-data controls that the agent cannot rewrite by its own reasoning. [1,5–6,17] Security and product teams use a separate policy decision point to test authority at each consequential tool call and preserve the policy version, timestamp, allow or deny result, and escalation reason. Finance keeps its own payment and accounting approvals; purchase-order creation does not transfer payment authority. Internal audit samples task origins, tokens, policy decisions, tool responses and exceptions against the same legal entity and effective period. An agent may operate autonomously inside a defined lower-risk scope; out-of-scope or higher-risk actions need a competent new decision. Repeated confirmation prompts can also produce approval fatigue. [1,3] The legal effect of an electronic document or signature remains conditional under Taiwan's Electronic Signatures Act and cannot be inferred from a log alone. [18]
證據、成果與影響
Evidence / Results / Impact證據鏈應按「來源可支持什麼」拆開,而不是把十九個連結寫成共同背書。NIST 2026 年十項設計原則屬初步技術提案;NCCoE 仍在規劃示範;FSB 十二項 sound practices 是金融業非強制建議;ICO 仍在徵求意見,截止日為 2026 年 11 月 20 日。[1–4] IETF RFC、W3C PROV-O 和可驗證憑證是技術規格,不是台灣企業交易的法源。[6–8] 歐盟 AI Act 的紀錄與人為監督規定取決於高風險系統分類、條文與施行時點,不因台灣供應商使用代理者就直接成為台灣法律義務。[9] 台灣端,《人工智慧基本法》是已施行法;行政院施行規劃是政策公告;數發部框架是跨部會分類工具;金管會原則與指引的對象及規範效力有其金融業邊界;《公司法》和《電子簽章法》要按實際公司及交易適用。[10–18] 《個人資料保護法》網頁列有部分 2025 年修正條文尚未生效,不能用最新全文頁面推定每一條都已生效。[19] 對個案的記錄可證明「何者被記下」,是否足夠、合法及可對外宣稱仍待有權者審查。
The evidence chain must state what each source supports, rather than imply that nineteen links jointly endorse one conclusion. NIST's 2026 tenets are initial technical proposals; NCCoE is developing demonstrations; the FSB's twelve sound practices are non-binding financial-sector recommendations; and the ICO consultation remains open until 20 November 2026. [1–4] IETF and W3C specifications concern technical representation and provenance, not Taiwan corporate transaction law. [6–8] The EU AI Act's record-keeping and human-oversight provisions depend on high-risk classification, applicable articles and implementation timing. A Taiwan supplier does not acquire an identical local statutory obligation merely by using an agent. [9] In Taiwan, the AI Basic Act is enacted law; the Executive Yuan implementation plan is a policy announcement; the digital ministry's framework is a cross-agency risk vocabulary; FSC guidance has a financial-sector scope; and the Company Act and Electronic Signatures Act require transaction-specific application. [10–18] The Personal Data Protection Act page warns that parts of the 2025 amendment have not yet commenced. Its latest consolidated text must not be read as if every provision were effective. [19] A record can show what was captured. Sufficiency, lawfulness and permission to make a public claim remain questions for authorised reviewers.
產業與制度意涵
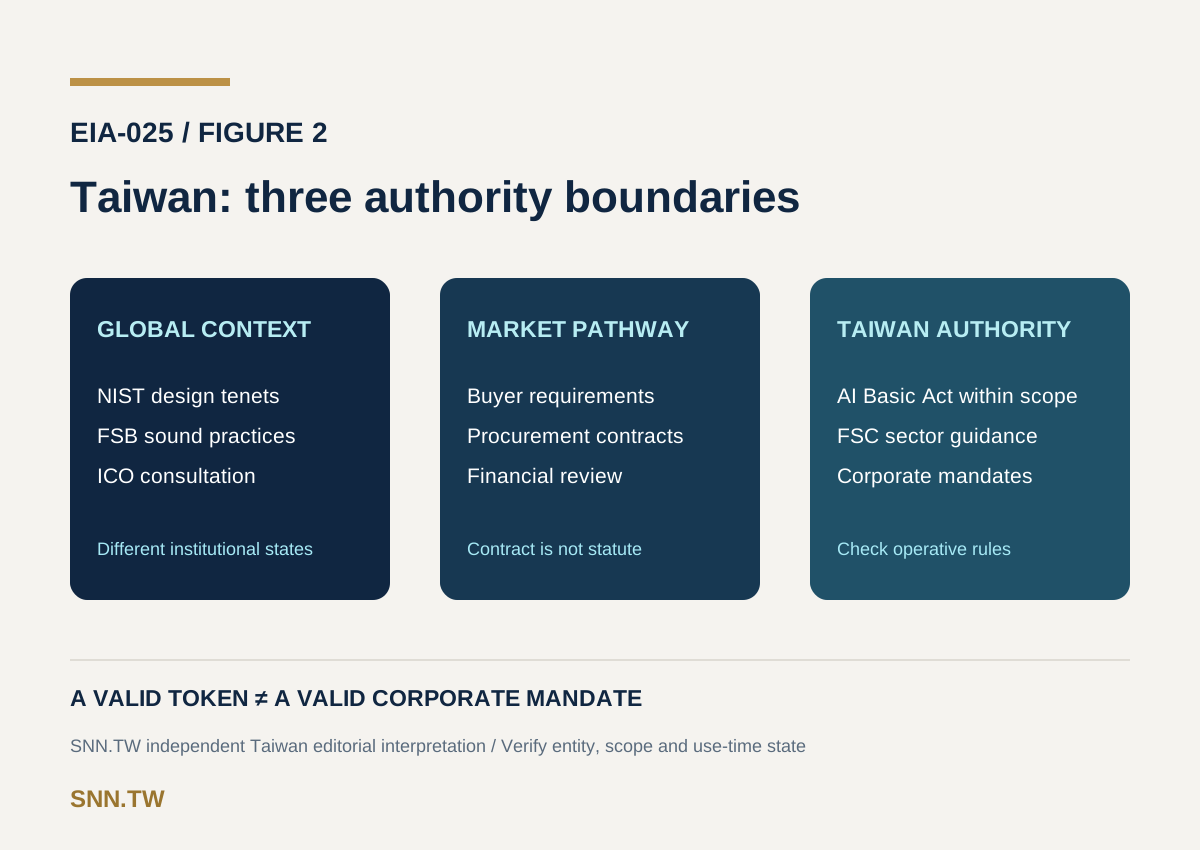
Industry & Institutional Implications台灣市場傳導至少有三條路。第一,出口製造與科技供應商的國際客戶可能在採購契約中要求說明代理者何時可篩選合格供應商、簽發訂單或更改交付資訊;這是契約與驗收需求,不等於一律法定揭露。第二,銀行、投信與保險機構導入 AI 協助客戶服務、授信或內控時,會碰到金管會金融業指引、既有內控、自然人數位身分及個資處理的不同適用範圍,金融機構仍須自行作風險與權限判斷。[13–16,19] 第三,上市櫃企業若讓代理者生成董事會資料、申報草稿或 ESG 主張,責任編輯、財務、法務與董事會需辨識誰能核准內容;工具生成與正式披露是兩個事件。海外採購方宜要求交易層的委任主體、額度、政策版本、工具日誌和異常補救記錄,而不是只看供應商宣稱「AI 已驗證」。上述機制可能提高資料交接成本,但並不證明特定企業已部署或符合任何國際準則。
Three transmission pathways are material in Taiwan. First, an overseas buyer may use a procurement contract to ask a manufacturing or technology supplier when an AI agent may screen vendors, issue an order or change delivery data. This is a contractual and acceptance question, not a universal Taiwan statutory disclosure duty. Second, a bank, asset manager or insurer using AI for customer service, credit or internal controls faces the different scopes of FSC financial guidance, existing controls, natural-person digital identity and personal-data processing. The institution retains its own risk and authority decisions. [13–16,19] Third, if a listed issuer lets an agent prepare board papers, filing drafts or sustainability claims, its editorial, finance, legal and board functions must distinguish tool output from authorised disclosure. International procurers should ask for the transaction-level principal, ceiling, policy version, tool log and exception record, rather than accepting a generic assertion that “AI verified” the workflow. These pathways may create evidence handoff costs. They do not establish that a particular Taiwan company has deployed an agent or complied with any international framework.
SNN 編輯與揭露前證據基礎設施觀點
SNN Editorial / Pre-Disclosure Evidence Infrastructure Perspective全球 NIST 在 2026 年 10 月更新代理身分與授權的初步制度設計原則,FSB 同月發布金融業 AI 治理非強制實務,英國 ICO 正就代理式 AI 的個資監理徵詢意見;這些全球制度變動可能透過跨境客戶的採購合約、金融審查及供應鏈系統權限要求傳導,令台灣製造、科技與金融企業在訂單、資料存取及揭露前增加對委任範圍、執行時權限和操作紀錄的核對需求。[1–4] 這是有條件的市場傳導,不代表國外文件直接創設台灣法定義務;台灣《人工智慧基本法》、金管會指引與公司權限各須按自己的法域狀態和適用對象查核。[10,13–18] SNN Editorial / 揭露前證據基礎設施(Pre-Disclosure Evidence Infrastructure)觀點的事實邊界:有效憑證不等於有效企業委任。法務與董事會辦公室應在代理者首次取得採購權限前核對決議、章程與委任文件,記錄授權人、額度、期限及撤銷條件。採購與資訊安全團隊應在每次關鍵下單或工具呼叫時保存政策版本、供應商名單、允許或拒絕決定與操作日誌,並在超界時交給有權人員重新判斷。財務與內部稽核部門應在每次付款放行或揭露前抽查交易憑證、權限變更與例外處理紀錄,將已執行和已核准分開。確信者與監理機關只在其法定或受委任範圍作判斷,不由代理者或本篇替代。本篇禁止推論:代理者登入成功並完成訂單,不證明任務發起人有公司授權、付款有效或成果已獲審查。
In October 2026, NIST updated initial global institutional design tenets for agent identity and authorisation, the FSB introduced non-binding financial-sector AI governance practices, and the UK ICO opened an agentic-AI privacy consultation. Those global institutional changes may transmit through overseas customer procurement contracts, financial review and supply-chain access requirements, creating more granular pre-disclosure evidence demands for Taiwan manufacturing, technology and financial companies on order authority, data access and runtime control. [1–4] This is conditional market transmission, not a claim that foreign materials themselves impose Taiwan statutory duties. Taiwan's AI Basic Act, FSC guidance and corporate-authority rules retain their own legal states and addressees. [10,13–18] The SNN Editorial / Pre-Disclosure Evidence Infrastructure Perspective is an independent editorial interpretation. Its fact boundary: A valid credential does not establish a valid corporate mandate. Before an agent first receives procurement privileges, legal and the board office should reconcile resolutions, articles and mandate documents, recording the principal, limit, period and revocation condition. At each consequential order or tool call, procurement and security teams should preserve the policy version, eligible-supplier list, allow or deny decision and operation log, escalating an out-of-scope action to competent staff. Before each payment release or public disclosure, finance and internal audit teams should sample transaction documents, changed permissions and exception records, keeping executed actions separate from approved decisions. An assurance provider or regulator judges only within its own mandate; neither the agent nor this article makes that decision. Prohibited inference for this edition: A successful login and completed order do not prove that the task originator held corporate authority, that payment was valid or that an outcome was reviewed.
未來展望
Future Outlook下一階段應追蹤三種可驗證變化:企業是否能在撤銷授權後阻止舊權杖執行、跨系統紀錄是否能重建同一行動的授權時點,以及人為升級是否真正處理例外而非形式點選。這些是待檢驗的研究問題,不是任何產品或組織已通過測試的宣稱。台灣主管機關後續可能按產業訂定更具體規範,應以正式公布的法令或函令更新狀態,而不是以新聞公告或海外標準自行升級。[10–12] 企業亦須核對個資法修正部分條文的施行日期。[19] 本稿保留來源查核、法域、支持範圍與限制供人類編輯覆核;公開及法律結論仍須完成本站既有審查與發布程序。
The next stage should test three questions: whether revocation prevents old credentials from completing an action, whether records across systems can reconstruct the authority effective at the action time, and whether human escalation genuinely resolves exceptions rather than inviting habitual approval. These are research propositions, not a claim that any product or institution has passed such a test. Taiwan's sectoral authorities may later issue more specific instruments. Any legal-state escalation must follow formally published rules or orders rather than a news notice or foreign standard. [10–12] Enterprises should also check commencement dates for the uncommenced parts of the Personal Data Protection Act amendment. [19] This draft preserves source dates, jurisdiction, support scope and limitations for human editorial review. Public release and legal conclusions remain subject to SNN.TW's existing source, editorial and publication governance.
來源、證據鏈與責任編輯
來源媒體:Sustainability News Network / Global Canonical · 原文作者:Anderson Yu · 原文發布:
原始出版
外部論述與制度來源
以下外部公告、法規、研究或新聞用於支撐本文論述,並與原始出版分開呈現。
- Primary anchor: official NIST design tenets, non-binding proposalNISTDesign Tenets for Agent Identity Management Systems ↗出版日期 2026-10-27 · 查核時間 2026-11-10 23:33 (UTC+8)
Ten initial agent identity, delegation and independent evidence design tenets
State: CONTEXT_ONLY · Jurisdiction: Global
Support scope: Initial design proposals for agent authorisation
Limitation: Technical blog proposals, not mandatory rules
- Global project contextNIST NCCoEComments on Software and Agentic SI Identity Concept Paper ↗出版日期 2026-09-29 · 查核時間 2026-11-10 23:33 (UTC+8)
Project feedback and planned demonstration use case
State: CONTEXT_ONLY · Jurisdiction: Global
Support scope: Identity and authorisation research status
Limitation: Demonstration plan does not verify any company deployment
- Primary anchor: FSB final sound practices, non-bindingFinancial Stability BoardSound Practices for Responsible Adoption of Artificial Intelligence: Final Report ↗出版日期 2026-10-15 · 查核時間 2026-11-10 23:33 (UTC+8)
Twelve financial-sector governance and oversight sound practices
State: CONTEXT_ONLY · Jurisdiction: Global
Support scope: Financial-sector non-binding governance context
Limitation: Recommendations are not universal corporate law or Taiwan regulation
- Privacy consultationUK Information Commissioner’s OfficeAgentic AI Call for Evidence ↗出版日期 2026-10-08 · 查核時間 2026-11-10 23:33 (UTC+8)
Open consultation on agentic AI privacy, transparency and accountability
State: CONTEXT_ONLY · Jurisdiction: United Kingdom
Support scope: Open consultation, closing 2026-11-20
Limitation: Consultation is not final guidance or Taiwan law
- Access-control architectureNISTSpecial Publication 800-207: Zero Trust Architecture ↗出版日期 2020-08-11 · 查核時間 2026-11-10 23:33 (UTC+8)
Distinguishes access decisions and continuous evaluation
State: GLOBAL_STANDARD · Jurisdiction: Global
Support scope: Technical architecture reference
Limitation: Does not grant substantive corporate authority
- Delegation specificationIETFRFC 8693: OAuth 2.0 Token Exchange ↗出版日期 2020-01-15 · 查核時間 2026-11-10 23:33 (UTC+8)
Subject and actor token exchange, impersonation and delegation
State: GLOBAL_STANDARD · Jurisdiction: Global
Support scope: Technical token and delegation representation
Limitation: Token validity cannot decide corporate mandate or legal effect
- Provenance specificationW3CPROV-O: The PROV Ontology ↗出版日期 2013-04-30 · 查核時間 2026-11-10 23:33 (UTC+8)
Provenance relationships among entity, activity and agent
State: GLOBAL_STANDARD · Jurisdiction: Global
Support scope: Data model for provenance
Limitation: A provenance relation does not certify factual truth or authority
- Credential specificationW3CVerifiable Credentials Data Model v2.0 ↗出版日期 2025-05-15 · 查核時間 2026-11-10 23:33 (UTC+8)
Credential verification and claim-assessment distinction
State: GLOBAL_STANDARD · Jurisdiction: Global
Support scope: Technical credential model
Limitation: Verification of signature is not proof of the claim’s truth
- Foreign regulatory scopeEuropean UnionRegulation (EU) 2024/1689: Artificial Intelligence Act ↗出版日期 2024-07-12 · 查核時間 2026-11-10 23:33 (UTC+8)
Scope-bound records and human oversight for relevant high-risk systems
State: FOREIGN_RULE · Jurisdiction: European Union
Support scope: EU high-risk AI framework where applicable
Limitation: Formal EU regulation; phased applicability and classification required; no automatic Taiwan duty
- Primary anchor: Taiwan current binding AI statute, scope-specific全國法規資料庫/國科會人工智慧基本法 ↗出版日期 2026-01-14 · 查核時間 2026-11-10 23:33 (UTC+8)
台灣 AI 基本法已公布施行,政府與目的事業主管機關權責分工
State: CURRENT_BINDING_RULE · Jurisdiction: Taiwan
Support scope: 基本法原則及公部門適用條文
Limitation: 正式法規;不得推成所有民間 AI 代理動作均有同一直接法定核准程序
- Taiwan implementation state行政院人工智慧基本法施行規劃 ↗出版日期 2026-05-21 · 查核時間 2026-11-10 23:33 (UTC+8)
行政院說明部會法規調適與公部門內控期程
State: ANNOUNCED_CHANGE · Jurisdiction: Taiwan
Support scope: 政策施行及調適時程公告
Limitation: 新聞公告並非各產業已完成修法或直接企業義務
- Taiwan risk framework數位發展部訂定人工智慧風險分類框架並自即日生效 ↗出版日期 2026-07-07 · 查核時間 2026-11-10 23:33 (UTC+8)
跨部會風險分類框架發布及其適用目的
State: CONTEXT_ONLY · Jurisdiction: Taiwan
Support scope: 行政框架作為主管機關共通評估語言
Limitation: 框架生效不表示所有企業取得同一直接法定義務;仍看目的事業法規
- Taiwan finance guidance金融監督管理委員會金融業運用人工智慧(AI)指引 ↗出版日期 2024-06-20 · 查核時間 2026-11-10 23:33 (UTC+8)
金融業 AI 治理、風險與人為監督參考
State: VOLUNTARY_USE · Jurisdiction: Taiwan
Support scope: 金融業 AI 應用指引
Limitation: 屬金融業指引,不能外推所有產業或代替適用法規
- Taiwan finance principles金融監督管理委員會金融業運用人工智慧(AI)之核心原則與相關推動政策 ↗出版日期 2023-10-17 · 查核時間 2026-11-10 23:33 (UTC+8)
金融業 AI 核心原則及責任治理政策
State: VOLUNTARY_USE · Jurisdiction: Taiwan
Support scope: 金融業核心原則脈絡
Limitation: 政策原則不等於逐項 AI 交易已核准或所有產業法定義務
- Taiwan digital identity金融監督管理委員會金融服務業辦理數位身分驗證指引 ↗出版日期 2023-10-24 · 查核時間 2026-11-10 23:33 (UTC+8)
金融服務業自然人數位身分驗證邊界
State: VOLUNTARY_USE · Jurisdiction: Taiwan
Support scope: 金融服務業身分驗證指引
Limitation: 適用自然人數位身分服務,不自動認定 AI 代理者公司權限
- Taiwan access reference金融監督管理委員會金融業導入零信任架構參考指引 ↗出版日期 2024-07-15 · 查核時間 2026-11-10 23:33 (UTC+8)
金融業持續驗證與零信任參考架構
State: VOLUNTARY_USE · Jurisdiction: Taiwan
Support scope: 金融業零信任參考
Limitation: 技術驗證與企業授權是不同判斷,不代表已符合個案監理要求
- Taiwan corporate authority全國法規資料庫/經濟部公司法 ↗出版日期 2025-12-26 · 查核時間 2026-11-10 23:33 (UTC+8)
董事會與經理人權限須依公司法、章程與決議核對
State: CURRENT_BINDING_RULE · Jurisdiction: Taiwan
Support scope: 公司機關與經理人權限的法律脈絡
Limitation: 正式法規;近期修正條文另查施行狀態,不能以 API 權杖推定法定權限
- Taiwan electronic record全國法規資料庫/數位發展部電子簽章法 ↗出版日期 2024-05-15 · 查核時間 2026-11-10 23:33 (UTC+8)
電子文件與簽章效力、範圍及留存條件
State: CURRENT_BINDING_RULE · Jurisdiction: Taiwan
Support scope: 電子簽署及文件的形式條件
Limitation: 正式法規;簽章效力仍須符合適用條件,不自證企業交易授權
- Taiwan privacy transition全國法規資料庫/個資委員會籌備處個人資料保護法 ↗出版日期 2025-11-11 · 查核時間 2026-11-10 23:33 (UTC+8)
個資處理目的、安全及 2025 修正條文施行狀態
State: PENDING_AMENDMENT · Jurisdiction: Taiwan
Support scope: 個資法修正部分條文尚未生效的狀態區分
Limitation: 修正法規頁註明部分施行日期未定;現行義務須另核對舊法有效條文
主題中心:揭露前證據基礎設施